What Is an Application Delivery Controller (ADC)?
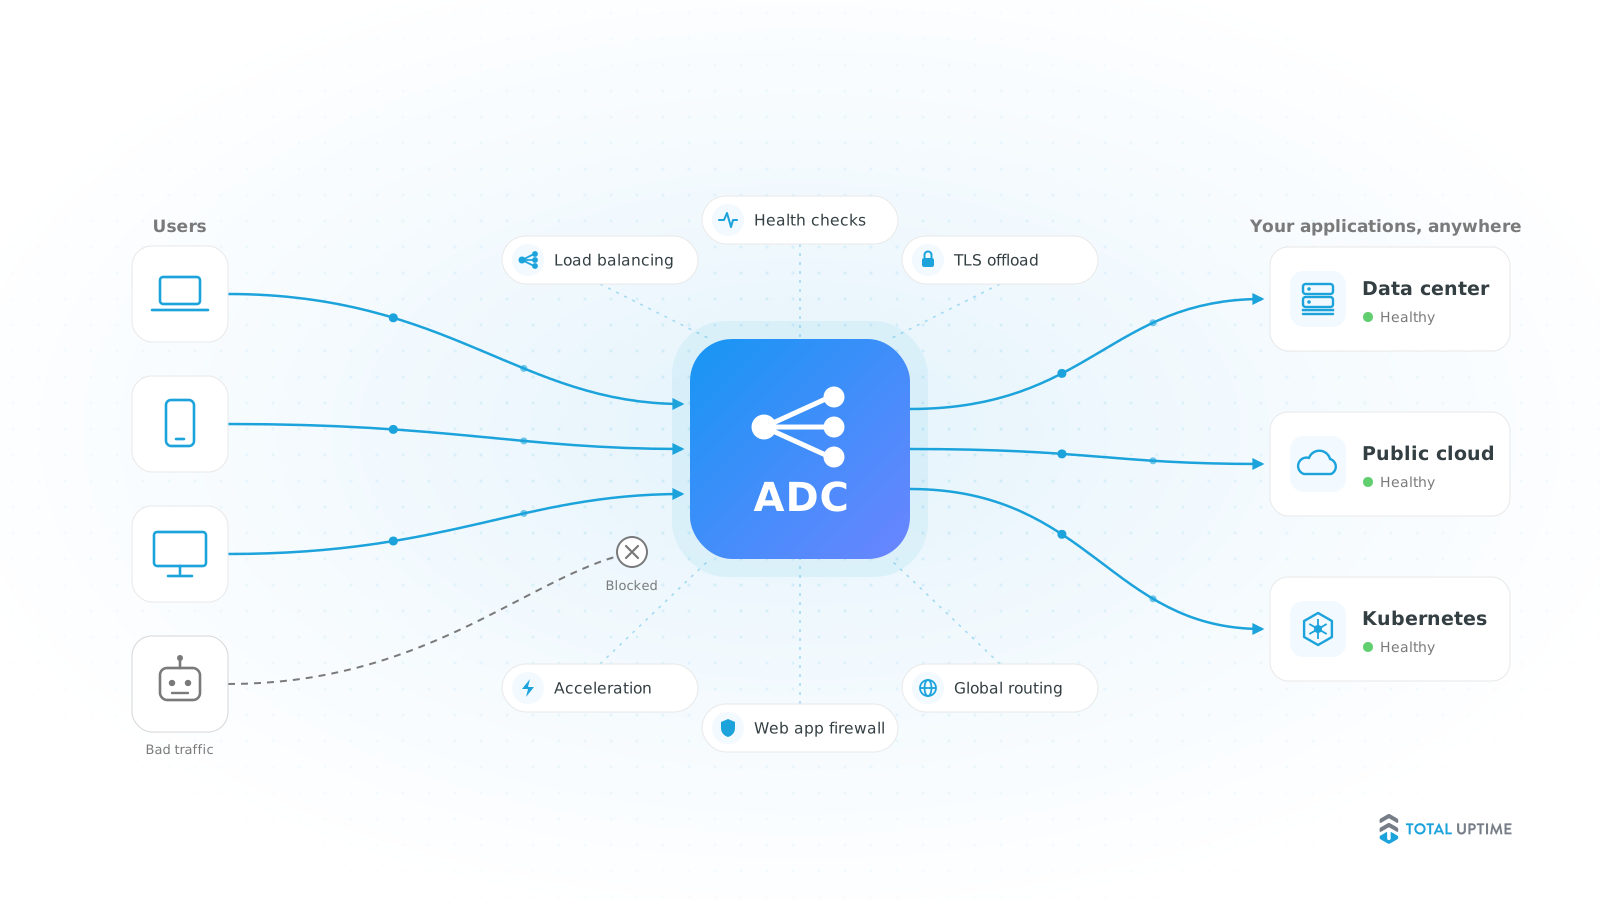
An application delivery controller (ADC) is a network service that sits between users and your application servers. It spreads traffic across healthy servers, handles TLS encryption, checks server health, speeds up responses and filters attacks, so applications stay available, fast and secure. ADCs run as hardware, virtual appliances, software or a managed cloud service.
ADCs grew out of load balancers. Today the ADC is the control point for how users reach an application: it decides which server answers each request, what happens when one fails, and which traffic never gets through. Application delivery is the wider practice of keeping applications reachable and fast; the ADC is the component that does most of the work.
How an application delivery controller works
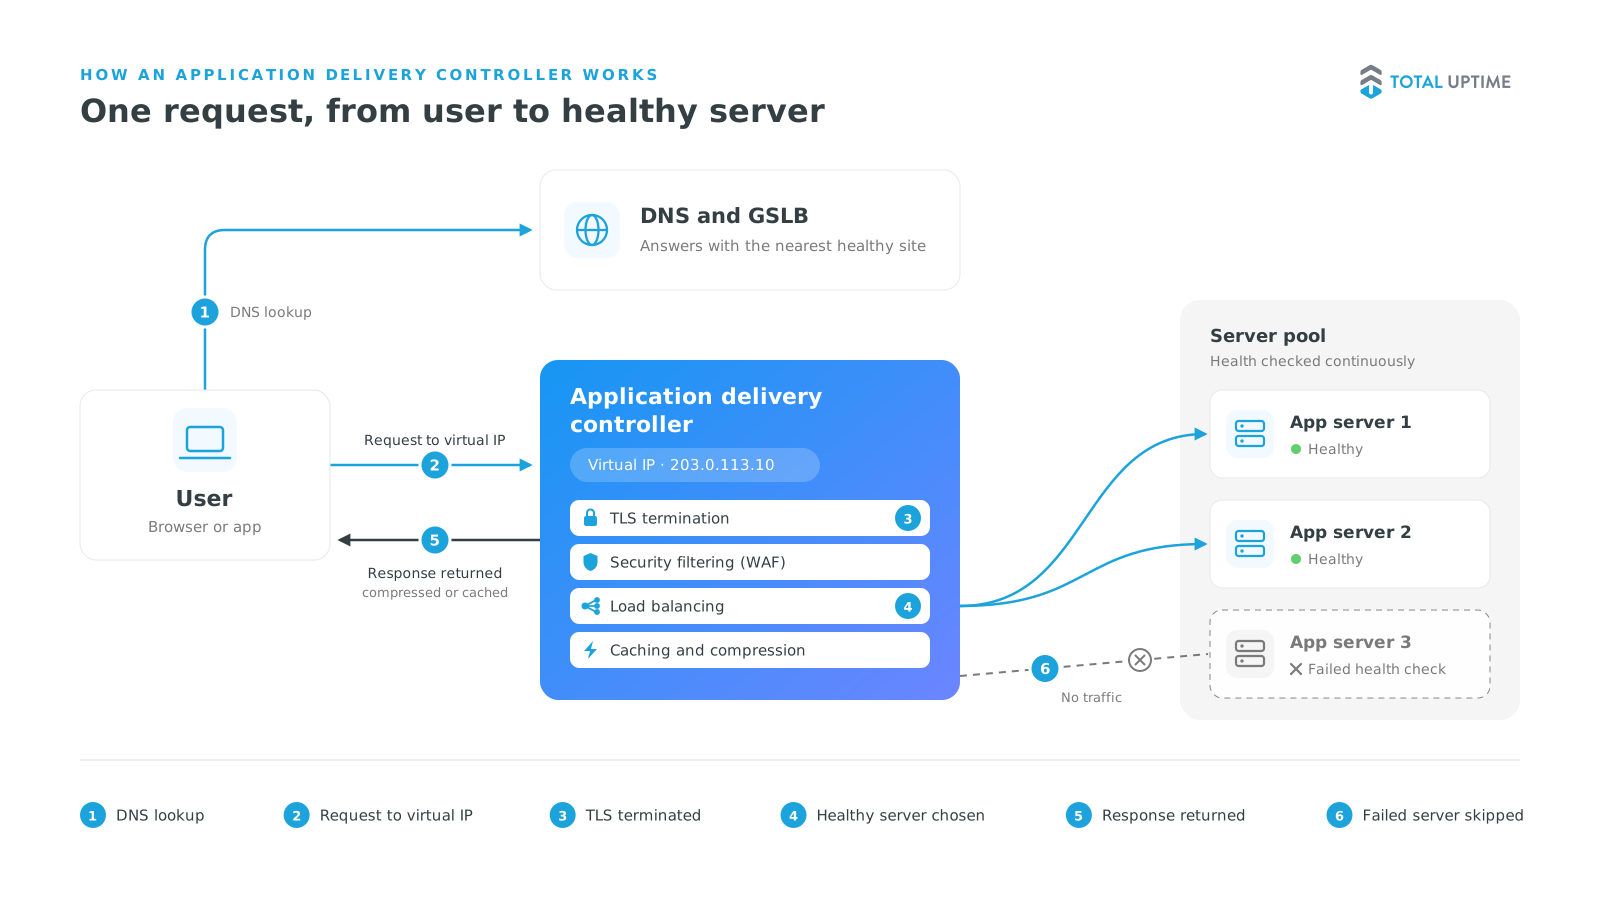
Follow one request from a user to your application:
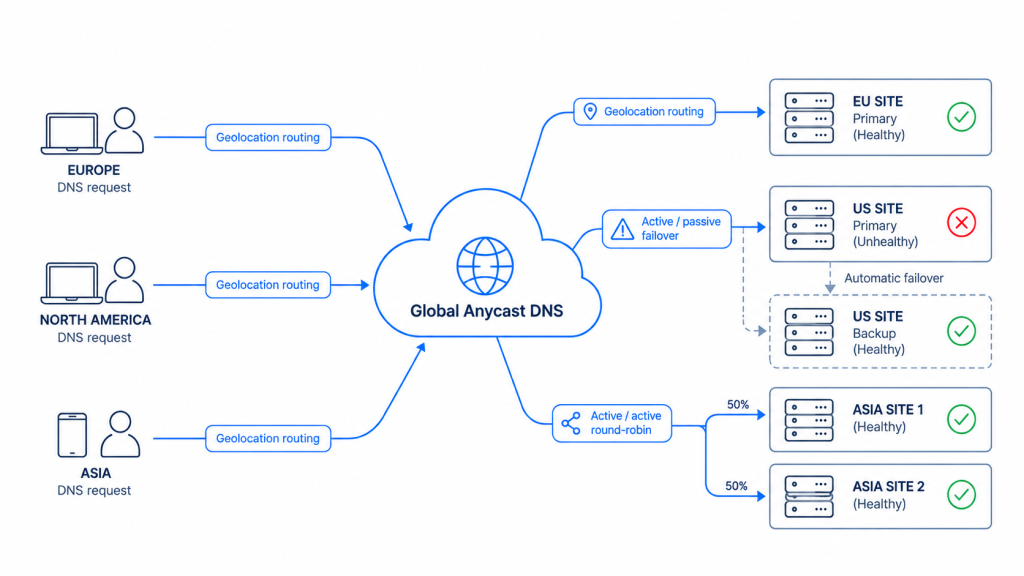
1. The user’s browser looks up your domain in DNS. With global server load balancing (GSLB), DNS can answer with the nearest healthy site.
2. The request reaches the ADC’s virtual IP address (VIP). Users only ever see this address, never the servers behind it.
3. If the connection is encrypted, the ADC can terminate TLS and read the request.
4. It picks a server from the pool, based on its load balancing method and the latest health checks.
5. It forwards the request and returns the response, often compressed or served from cache.
6. If a server fails a health check, the ADC stops sending it traffic until it recovers.
An ADC can make its routing decision at two levels of the OSI model. At Layer 4, the transport layer, it routes on IP address and port. That is fast and works for any TCP or UDP application. At Layer 7, the application layer, it reads the request itself (host name, URL path, headers or cookies), so it can send /api requests to one pool of servers and /images to another.
What an application delivery controller does
Every ADC covers six jobs. Products differ in how deep each one goes.
Load balancing
The ADC spreads requests across a pool of servers so that no single server is overloaded or becomes a single point of failure. Common methods include round robin (each server in turn), least connections (the server with the fewest active sessions), weighted distribution (larger servers take more traffic) and content-based routing. Session persistence, also called sticky sessions, keeps a user on the same server when the application needs it. For the fundamentals, see what load balancing is and whether you need it.
Health monitoring and failover
An ADC checks every server continuously. A check can be as simple as a ping or a TCP connection, or as specific as an HTTP request that expects a particular response within a set time. When a server fails, the ADC takes it out of rotation and users carry on without noticing. When it recovers, it rejoins the pool. The same principle works between data centers: see automated datacenter failover and how DNS failover works.
SSL/TLS offloading
Encrypting and decrypting traffic takes processing power. The ADC terminates TLS on behalf of every server behind it, so certificates are managed in one place and servers spend their capacity on the application. Where traffic must stay encrypted all the way, the ADC re-encrypts it before passing it on. Current ADCs support TLS 1.3.
Application acceleration
An ADC makes applications respond faster without changing them. It caches frequently requested content, compresses responses, and reuses a small number of server connections for many users (TCP multiplexing). Many ADCs also speak HTTP/2 to browsers while the servers behind them stay on HTTP/1.1.
Security
Every request passes through the ADC, which makes it a natural place to stop attacks. A web application firewall blocks attacks such as SQL injection and cross-site scripting, the kinds of risk listed in the OWASP Top 10. Access control lists, rate limits and connection limits help absorb denial-of-service attacks before they reach your servers; CISA’s guide to DDoS attacks explains the main types. Some ADCs also authenticate users before they reach the application.
Traffic management
Beyond choosing a server, an ADC can route by host name or URL, rewrite headers and URLs, redirect HTTP to HTTPS, and show a maintenance page during planned work. Across regions, global server load balancing sends each user to the nearest healthy site. Inside Kubernetes, an ingress controller plays the same role for containerized applications; the Kubernetes documentation on Ingress explains the model.
ADC vs load balancer
A load balancer distributes traffic across servers and removes failed ones. An application delivery controller does that too, then adds TLS offloading, acceleration, security and Layer 7 traffic control. Every ADC is a load balancer, but not every load balancer is an ADC.
Capability | Basic load balancer | Application delivery controller |
|---|---|---|
Spreads traffic across servers | Yes | Yes |
Health checks and failover | Yes | Yes |
Routing by URL, host or header (Layer 7) | Sometimes | Yes |
SSL/TLS offloading | Sometimes | Yes |
Caching, compression, TCP multiplexing | Rarely | Yes |
Web application firewall | No | Built in or integrated |
Global server load balancing | No | Often available |
In practice the terms blur. Many products sold as load balancers now include Layer 7 features, and many people say “load balancer” when they mean an ADC. The useful question is which of these jobs your applications need.
ADC deployment models
ADCs come in four forms. The functions are much the same; what changes is where the ADC runs and who looks after it.
Model | Where it runs | Who maintains it | Best suited to |
|---|---|---|---|
Hardware appliance | A dedicated device in your data center | Your team, with vendor hardware support | High, steady traffic in one location |
Virtual appliance (virtual ADC) | A virtual machine on your hypervisor or in a public cloud | Your team | Appliance features without dedicated hardware |
Software or container | Your servers, containers or Kubernetes clusters | Your team | DevOps teams automating delivery per application |
ADC-as-a-service | The provider’s network, in front of your applications | The provider | Teams that want the outcome without running the infrastructure |
A “global” ADC is not a fifth model: any of these can work across sites when it includes global server load balancing.
Total Uptime offers both ends of this range. ADC-as-a-service runs on our anycast network in front of applications on-premises, in colocation or in any cloud. edgeADC, our self-hosted ADC, gives your team Layer 4–7 load balancing, acceleration and security on your own infrastructure.
When do you need an ADC?
You probably need an ADC if any of these apply:
– You run an application on more than one server, or plan to.
– You have uptime commitments to customers or to internal users.
– You manage TLS certificates on many servers and want one place to do it.
– Your applications face the public internet and attract attacks.
– You serve users from more than one site, region or cloud. See how to increase application availability.
– Your hardware ADC is due for renewal or nearing end of life. Our comparisons with F5 and NetScaler set out the options.
Frequently asked questions
What does ADC stand for in networking?
In networking, ADC stands for application delivery controller: the service in front of your application servers that manages how users reach them. It balances load, offloads TLS, checks server health and filters attacks. In electronics, ADC means analog-to-digital converter, which is unrelated.
What is ADC in NetScaler?
NetScaler ADC is the application delivery controller made by NetScaler, now a business unit of Cloud Software Group. It was sold as Citrix ADC from 2018 until the NetScaler name returned in 2022. If you are weighing a NetScaler renewal, see our NetScaler comparison and our article on NetScaler vulnerabilities.
What is a virtual ADC?
A virtual ADC is ADC software packaged as a virtual machine. It runs on your own hypervisor or in a public cloud instead of on dedicated hardware, offers the same functions as an appliance, and can be scaled, copied or moved like any other virtual machine.
Where is an ADC deployed?
Traditionally, in the data center between the firewall and the application servers, often in a DMZ. Today ADCs also run in public clouds, inside Kubernetes clusters, and as a managed service in front of applications wherever they are hosted.
What is an ADC in cyber security?
An ADC is a traffic manager and a security control at once, because every request passes through it. It can terminate and inspect TLS traffic, run a web application firewall, block traffic by country or IP address, limit request rates and absorb denial-of-service attacks before they reach your servers.
Can I run an ADC as a managed service?
Yes. With ADC-as-a-service, the provider runs the ADC on its own network and you manage the configuration through a portal or API. Total Uptime’s ADC-as-a-service works with applications on-premises, in colocation or in any cloud.
Run your ADC managed or self-hosted
Total Uptime delivers ADCs both ways. ADC-as-a-service places a fully managed ADC in front of your applications. edgeADC runs on your own infrastructure. Compare managed pricing and self-hosted pricing, or talk to an engineer.